Launch & operations
From Prototype to Production: What Makes an App Ready for Real Customers?
A prototype can prove that an idea deserves attention. A first release must prove that a bounded version of that idea can carry responsibility when real people depend on it.
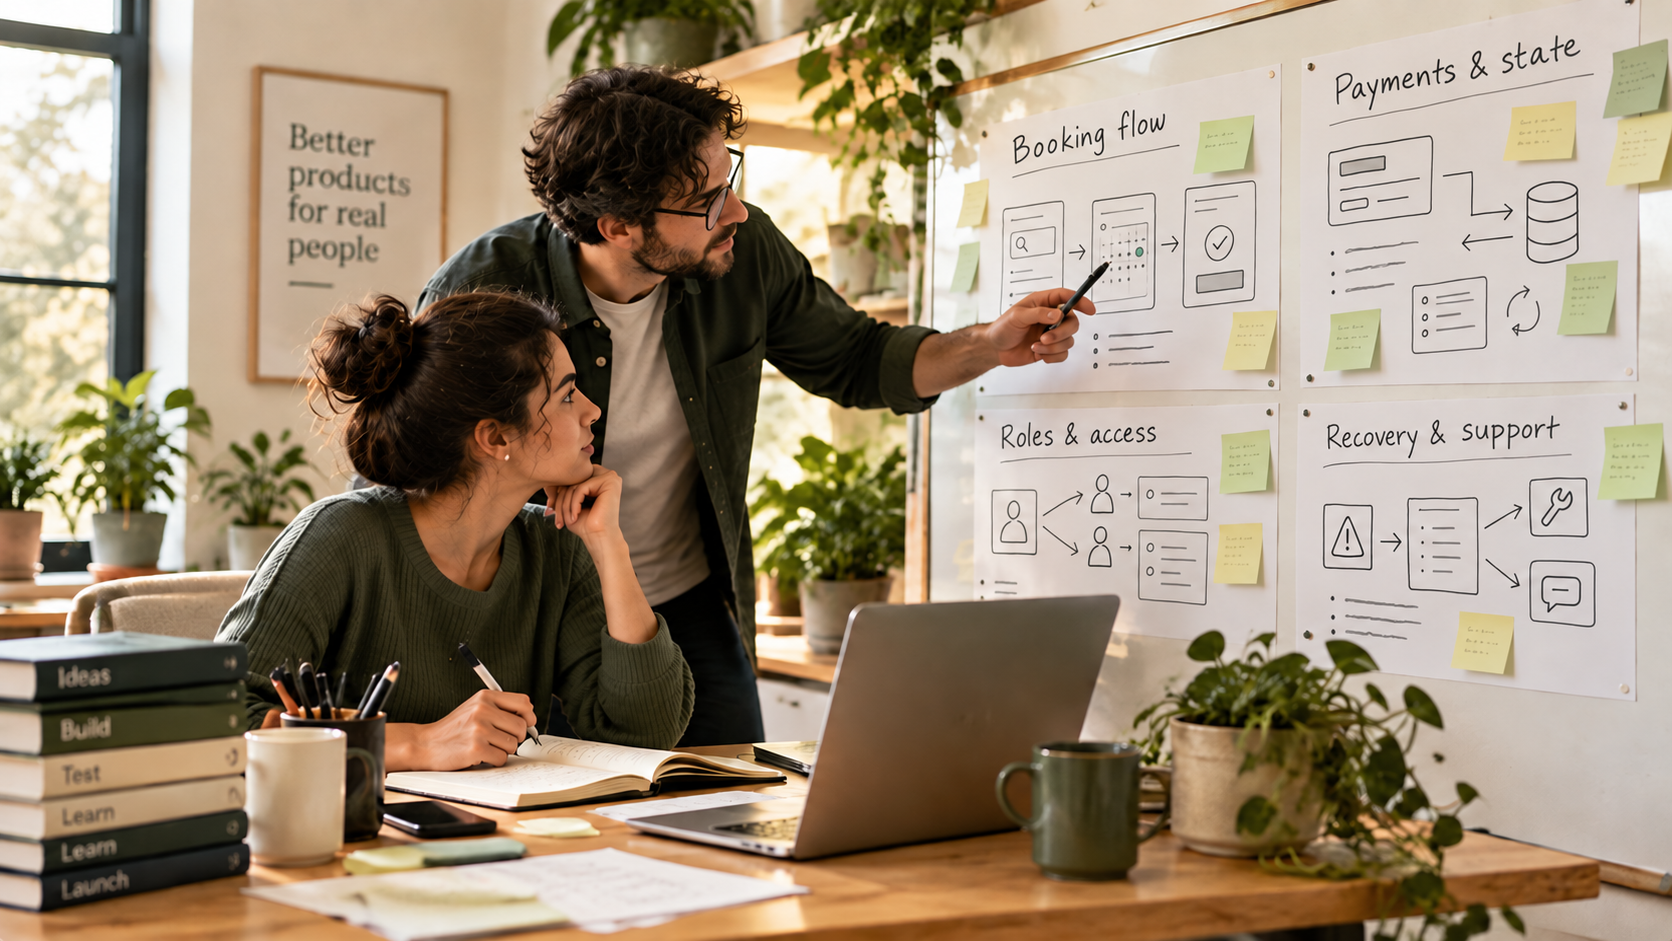
The moment a convincing demo becomes a real responsibility
A prototype has a special kind of power. It lets a founder move quickly enough to ask a question that would otherwise remain theoretical: does this idea make sense to another person?
That question matters. A good prototype can reveal that a workflow is confusing, that a feature nobody expected is actually the important one, or that a problem a founder considered urgent is not the problem users actually have. The prototype is valuable because it creates evidence before a team commits heavily.
Consider a fictional company called HarborLane Appointments. HarborLane is not a Racoben customer or a real business; it is a worked example of the decisions founders face. The company wants to help small neighborhood businesses manage appointments. Its first prototype is simple. A customer chooses a time, enters information, and sees a confirmation screen. A business owner can view a list of appointments.
The prototype succeeds. People understand the idea. The screens communicate the basic flow. The founder now has something much better than an assumption.
But the prototype has quietly avoided several responsibilities.
The confirmation screen says an appointment exists, but what exactly made it true? Did the customer merely request a time? Did the business accept it? Did payment happen? If the customer closes the browser before the final step, what should they believe? If the business cancels the appointment later, where does that change appear?
The prototype did not fail by avoiding these questions. It succeeded by making them unnecessary during early learning. The transition toward a real release begins when those questions stop being design exercises and become promises made to another person.
The UK Government Digital Service describes prototypes as tools for exploring and testing designs before committing to building a service. Its guidance explains that prototypes may intentionally differ from production systems, including by using different levels of technical completeness. That distinction exists because the purpose of a prototype is learning, not carrying every responsibility of a live service. See: https://www.gov.uk/service-manual/design/making-prototypes
The difficult judgment for a founder is knowing when an omission was a useful shortcut and when it has become a risk.
A working payment flow is more than a button
HarborLane’s next step is a limited pilot. Some businesses are willing to use the scheduling tool with real customers. The founder adds payment because certain appointments require a deposit.
The visible change seems small. A payment button appears. A customer completes checkout. The system displays that the appointment is paid.
Behind that simple experience is a state problem.
Payment providers and applications often communicate asynchronously. A payment system may notify an application that something happened after the customer has already moved on from the payment page. The application must interpret that information and decide what business state should change.
Stripe’s webhook documentation explains that webhook deliveries can be retried, delivery order is not guaranteed, and the same event can be delivered more than once. It recommends handling duplicate events safely rather than assuming each delivery represents a completely new action.
For a founder, the important idea is not a particular programming technique. It is the difference between a notification and a business outcome.
If Stripe sends the same payment event twice, that does not mean Stripe charged the customer twice. It means the application received the same information more than once and needs to make sure the intended result happens safely.
In HarborLane’s case, the intended result might be that a paid appointment receives access to the appropriate booking status. The application should be able to recognize that the payment information has already been handled instead of creating a second deposit record or confusing the customer with a duplicate confirmation.
This is also where founders need to separate two problems that can look similar from the outside.
A duplicate notification is a technical delivery problem. The system received information again.
An ambiguous booking state is a product decision problem. The customer does not know whether they have a confirmed appointment, a pending request, or a payment waiting for review.
A managed payment provider removes some difficult work. A founder does not need to build a card network or invent secure payment handling from the ground up. But managed services do not decide what a successful business outcome means.
The application still needs clear rules.
Does payment confirm the appointment automatically? Does a staff member approve the time first? What happens if payment succeeds while the appointment request cannot be fulfilled? What should the customer see?
Those are not merely engineering questions. The founder owns the customer promise. The engineer helps turn that promise into a system that behaves consistently.
A reasonable first release does not need every possible payment scenario solved forever. It does need the team to identify which states matter now and prove that the important transitions behave as intended.
The account that can log in is not automatically the account that can do everything
HarborLane encounters a second transition when businesses ask for multiple staff members.
The prototype assumed one business owner. A production system may involve reception staff, managers, contractors, and customers. Information that was harmless in a demonstration now has an owner.
This is where authentication and authorization become separate concerns.
Authentication answers whether an account or session has successfully identified itself to the system. It does not, by itself, answer whether that account should be allowed to perform a particular action on a particular record.
OWASP’s guidance on broken object-level authorization describes authorization as a check involving the current user, the requested action, and the specific object being accessed.
For HarborLane, that distinction creates ordinary business decisions.
A customer may be allowed to view their own appointment details. A staff member may be allowed to update appointments assigned to the business. A manager may be allowed to change staff permissions. A former employee may no longer have access after their role ends.
The founder decides what these relationships should mean.
The engineer proves that the system consistently enforces those decisions.
That separation matters because many permission failures begin before code exists. The system cannot enforce a rule that nobody has clearly defined. “Managers can manage appointments” sounds simple until the team asks whether that includes deleting records, changing payment information, viewing customer notes, or adding another employee.
A production conversation turns vague roles into specific responsibilities.
For a small pilot, the answer may intentionally be narrow. Perhaps only managers can edit appointments at first. Perhaps staff members can view schedules but cannot modify payment information. That is not a sign that the product is incomplete. It is a deliberate boundary.
The evidence of readiness is not that every future permission exists. It is that the permissions that matter for the current release are understood, documented, and tested.
The temptation to build too much
At this point in HarborLane’s journey, the founder faces the most reasonable objection to all of this caution: perhaps the team is thinking too far ahead.
A product with very few users may not need elaborate systems. A founder who has not yet proven demand can waste months preparing for failures that may never occur. A carefully designed prototype can become trapped in endless refinement while a simpler version in front of real people would have produced more useful information.
That objection is correct.
There are many situations where custom software is the wrong first move. A small business testing whether customers want online booking may be better served by existing scheduling software. A team validating an internal process may learn more from a spreadsheet, a shared document, or a manual workflow than from building an application immediately.
The question is not whether custom software is more sophisticated. The question is whether the problem has become specific enough that adapting an existing tool creates more friction than solving the problem directly.
For HarborLane, an existing booking service might be the right choice if the business only needs standard appointments, basic reminders, and ordinary payment collection. Buying an established tool could provide reliability without forcing the founder to own every technical decision.
The calculation changes when the workflow itself becomes the product. If the business depends on unusual scheduling rules, specialized customer records, unique staff coordination, or a process that existing tools repeatedly distort, custom development may become justified.
Even then, a smaller release can be the better decision. A team can build the smallest part of the unique workflow that creates meaningful value while leaving ordinary capabilities to managed services or manual processes.
The mistake is not moving quickly. The mistake is confusing speed with avoiding responsibility.
A founder can move quickly with a managed tool. A founder can move quickly with a manual pilot. A founder can move quickly with custom software. Each choice creates a different set of obligations.
Once real people are involved, some responsibilities exist regardless of the technology choice. If customers provide personal information, someone must understand who can access it. If people depend on appointment times, someone must know how changes are communicated. If money changes hands, someone must know what the customer is entitled to receive.
The technology can change. The responsibility does not disappear.
The hidden system behind a manual process
HarborLane decides not to automate every unusual case immediately. During the pilot, the founder keeps one part of the appointment process manual.
This is not a temporary accident. It is a deliberate operating decision.
When a customer requests an appointment that requires a staff review, the system records the request. A designated operations owner checks those requests each morning, confirms available times with the business, and updates the customer-facing status.
The process has boundaries. One person owns the review. If that person is unavailable, another named team member handles the queue. Customers receive a clear explanation that their request is pending confirmation rather than assuming the appointment is final.
The team also needs a decision point for capacity. The purpose of the pilot is not to prove that a founder can personally absorb every exception forever. If requests begin accumulating faster than the owner can review them accurately, if customers cannot receive clear updates, or if reconciliation work starts competing with the normal operation of the business, the team has evidence that the current process boundary has been reached. At that point HarborLane may pause additional exposure, narrow the pilot, improve the workflow, or automate a specific bottleneck. The trigger is not a universal number of users; it is whether the process still produces reliable outcomes for the people already depending on it.
The team also keeps a simple reconciliation habit: requests received, appointments confirmed, cancellations processed, and payments requiring review must match the records the business uses.
This kind of process can work well at a small scale because everyone understands the human step.
The danger appears when the process exists only in someone’s memory.
A founder who personally checks every unusual booking may believe the software is simple. In reality, the founder may be performing the missing system. They know which customers need follow-up, which exceptions matter, and which situations require judgment.
That knowledge is valuable, but it is also a hidden dependency.
Turning that experience into software does not mean replacing the human immediately. It means learning what the human is actually doing.
Perhaps the founder is approving requests. Perhaps they are resolving conflicts between calendars. Perhaps they are noticing information the original prototype never captured. Those discoveries help determine what deserves automation and what should remain a deliberate human decision.
The goal is not to eliminate people from the process. The goal is to avoid a process that only works because one person remembers everything.
Recovery is part of the product experience
Before HarborLane accepts real pilot dependence, another question becomes unavoidable: what happens when important information cannot be reached? A small pilot does not remove the need for a proportionate recovery understanding. The scale of the process can be smaller, but the team still needs to know what information matters, who owns restoration decisions, and how customer commitments will be reconciled if a gap appears.
This is where many teams misunderstand backups. A backup is not only a technical object. It represents a future promise that the business can recover from a failure.
A copy of data is useful only if the team understands what it contains, who can restore it, and whether the restoration process actually works.
GitLab’s January 31, 2017 database outage is a useful historical example. In its postmortem, GitLab described a recovery effort complicated by failed backup procedures, including a failed pg_dump process using an older PostgreSQL version, rejected failure notification emails, and replication problems. A manually created staging snapshot became the recovery source, while slow copying extended restoration work. GitLab identified the absence of regular recovery testing and ownership as an important lesson. See the GitLab postmortem of the January 31 database outage.
The lesson for HarborLane is not that a small scheduling company needs GitLab’s architecture. It is that recovery is a chain, not a checkbox.
A founder should understand what restoration is expected to recover and what it cannot recover. If appointment records are restored but recent customer communications are not, what happens next? If a payment record is recovered but a confirmation message is missing, who determines the correct customer state?
HarborLane does not need a fictional promise that nothing can ever fail. It needs a realistic recovery conversation.
The team might decide that the first release requires a tested process for restoring a representative copy of appointment data. It might document who investigates missing records. It might define how pending bookings are reconciled against payment information after an interruption.
The important outcome is not simply having more copies.
It is knowing what those copies mean.
A pilot is still a real service
The idea of a pilot can create another misunderstanding. Some teams treat a limited release as if the rules do not apply yet because the audience is small.
That is not what a pilot means.
GOV.UK describes beta phases as a way to work with real users while improving a service, including considerations such as support, privacy, security, and accessibility. Source: GOV.UK How the beta phase works
A limited audience reduces exposure. It does not make users imaginary.
HarborLane’s pilot might begin with a small group of businesses. It may intentionally exclude advanced scheduling rules. It may keep some review steps manual. Those boundaries can be sensible.
But the team still needs to solve the whole problem it has chosen to address.
GOV.UK’s service standard emphasizes solving a whole user problem and considering existing solutions where appropriate rather than attempting to solve everything at once. Source: GOV.UK Solve a whole problem
For HarborLane, solving the whole problem does not mean building every possible scheduling feature. It means that the chosen journey works honestly.
A customer should understand whether an appointment is requested or confirmed. A business should understand which actions require staff attention. The team should know which parts are intentionally manual and which parts the software owns.
That is a complete small journey.
Evidence before trust
Returning to HarborLane's release decision, the team needs a way to distinguish confidence from evidence. A successful demonstration is useful evidence that the workflow can be represented. It is not evidence that every important transition will behave correctly under real conditions.
For the fictional pilot, the founder and engineer might examine specific behaviors. They might replay a previously processed payment notification against the same booking record and confirm that the intended booking state does not become confused by receiving the same information again. They might examine a delayed or reordered event and verify that the current customer-facing state still reflects the business decision that was actually made.
The same principle applies to access and recovery. The team might test two separate authorization decisions: that a staff member whose role is removed can no longer perform the actions that role previously allowed within HarborLane, and that a user from one business cannot access another business's records even when attempting to interact with similar objects. Those are different boundaries. One concerns a change in an account's permitted role; the other concerns isolation between separate customers or organizations. It might restore a representative copy of application data and determine which recent commitments require reconciliation afterward. These exercises are evidence about a particular design and process. They are not guarantees that every future failure has been eliminated.
The founder decides what evidence matters because the founder owns the customer promise. The engineer helps demonstrate whether the system behaves according to those decisions. A booking product does not become dependable because a checklist was completed; it becomes more dependable when the team can explain why important states, permissions, and recovery paths behave as intended.
Deciding what the first release means
HarborLane’s first release decision is not a declaration that the product is finished. It is a statement about what the team is prepared to support.
The founder may leave some decisions manual:
- unusual appointment conflicts;
- edge cases that require human judgment;
- workflows that have not happened often enough to automate safely.
The founder may require proof before releasing other parts:
- that customers see accurate appointment states;
- that permissions match business roles;
- that important records can be recovered through a known process.
The founder may exclude features entirely:
- complex reporting;
- uncommon integrations;
- automation that adds convenience without solving the core problem.
The decision to release is therefore not a test of whether the product has become large enough. It is a test of whether the team understands the promises it is making.
The most useful question is not “Is this production-ready?” as though production were a finish line with a universal definition.
The better question is “What are we asking people to depend on, and have we designed responsibly for that dependence?”
That question gives founders room to experiment without pretending experiments and commitments are the same thing.
Racoben’s engineering approach centers on helping organizations think through product ideas, technical decisions, and custom software development with a defined scope: Racoben Engineering